
Supporting our young men and bettering our community
Community Development Corporation
Supporting our young men and bettering our community
Community Development Corporation
If you are searching for the most exciting new casino online canada has to offer, you’re in the right place. Online gambling has exploded in popularity across the country, especially with the rise of technology and improvements to internet connectivity. This article will guide you through the latest and greatest online casinos available to Canadians, detailing what you should look for when choosing a platform to play your favorite games.
Online casinos have transformed the gambling landscape in Canada. With more people than ever embracing the convenience of playing from home, it is essential to understand what makes a new online casino stand out. Gamblers are attracted to the innovation and variety provided by new platforms that offer the latest gaming technology, unique bonuses, and an expansive selection of games.
When selecting a new online casino in Canada, consider several critical factors:
Here are some of the most promising new online casinos in Canada that you should consider:
Casino XYZ has quickly gained popularity for its user-friendly interface and extensive game library. Players can enjoy over 800 games, including a plethora of slots and table games. Their welcome bonus offers a 100% match on the first deposit, making it an enticing choice for newcomers.
With a strong focus on player experience, Casino ABC provides a range of bonuses tailored to various types of players. Their VIP program rewards loyal customers with exclusive promotions and faster withdrawals. They also feature a robust selection of live dealer games for those looking for an authentic casino atmosphere.
Casino 123 distinguishes itself with an extensive mobile platform, allowing players to enjoy their games on the go. Their app is compatible with both iOS and Android devices, providing a seamless gaming experience. Additionally, their generous cashback offers make it a favorite among regular players.
As mobile devices become more integral to our daily lives, online casinos have adapted by offering mobile-friendly platforms and apps. Most new online casinos prioritize mobile accessibility, ensuring that players can enjoy a full gaming experience regardless of where they are. The ability to play slots, table games, and even interact with live dealers from your mobile device enhances convenience and social interaction.
One of the most appealing aspects of new online casinos is their promotional offers. Most platforms provide a range of bonuses designed to attract new players. Here are some common types of promotions you might find:
Payment options vary widely between online casinos, but the best sites feature a range of secure and convenient options. Be sure to check for popular methods like Visa, Mastercard, Interac, PayPal, and newer cryptocurrencies like Bitcoin and Ethereum. Fast withdrawal times and low fees are also indicators of a good casino.
Safety is paramount when it comes to online gambling. Look for casinos that use encryption technology to protect personal information and have measures in place to ensure fair play, such as Random Number Generators (RNGs) that guarantee game outcomes are random and unbiased.
The landscape of online gambling in Canada is vibrant and ever-evolving, with new casinos constantly appearing on the scene. By following the guidelines outlined in this article, you can ensure you choose the right platform to enjoy your gaming experience. Always stay updated on new casinos, their bonuses, and game offerings to keep your online gambling experience fresh and exciting.
In conclusion, the world of online gambling in Canada is full of opportunities and excitement. Whether you are a seasoned player or a newcomer, there are countless options to explore. The key is to remain informed and choose platforms that prioritize your gaming experience and security.
Many DeFi users assume the difficult part of using several blockchains is remembering different networks. In practice, the more consequential problem is deciding what a transaction will do before signing it. A wallet may hold the same kind of asset across Ethereum and several EVM-compatible networks, yet the meaning, cost, permissions, and risk of a transaction can differ sharply from one chain to another.
That is why choosing and installing a multi-chain wallet deserves more thought than simply finding a convenient Rabby extension download. The useful question is not only whether a wallet can connect to many networks. It is whether the wallet helps a user understand contracts, token approvals, gas requirements, and likely outcomes at the moment a decision is made.
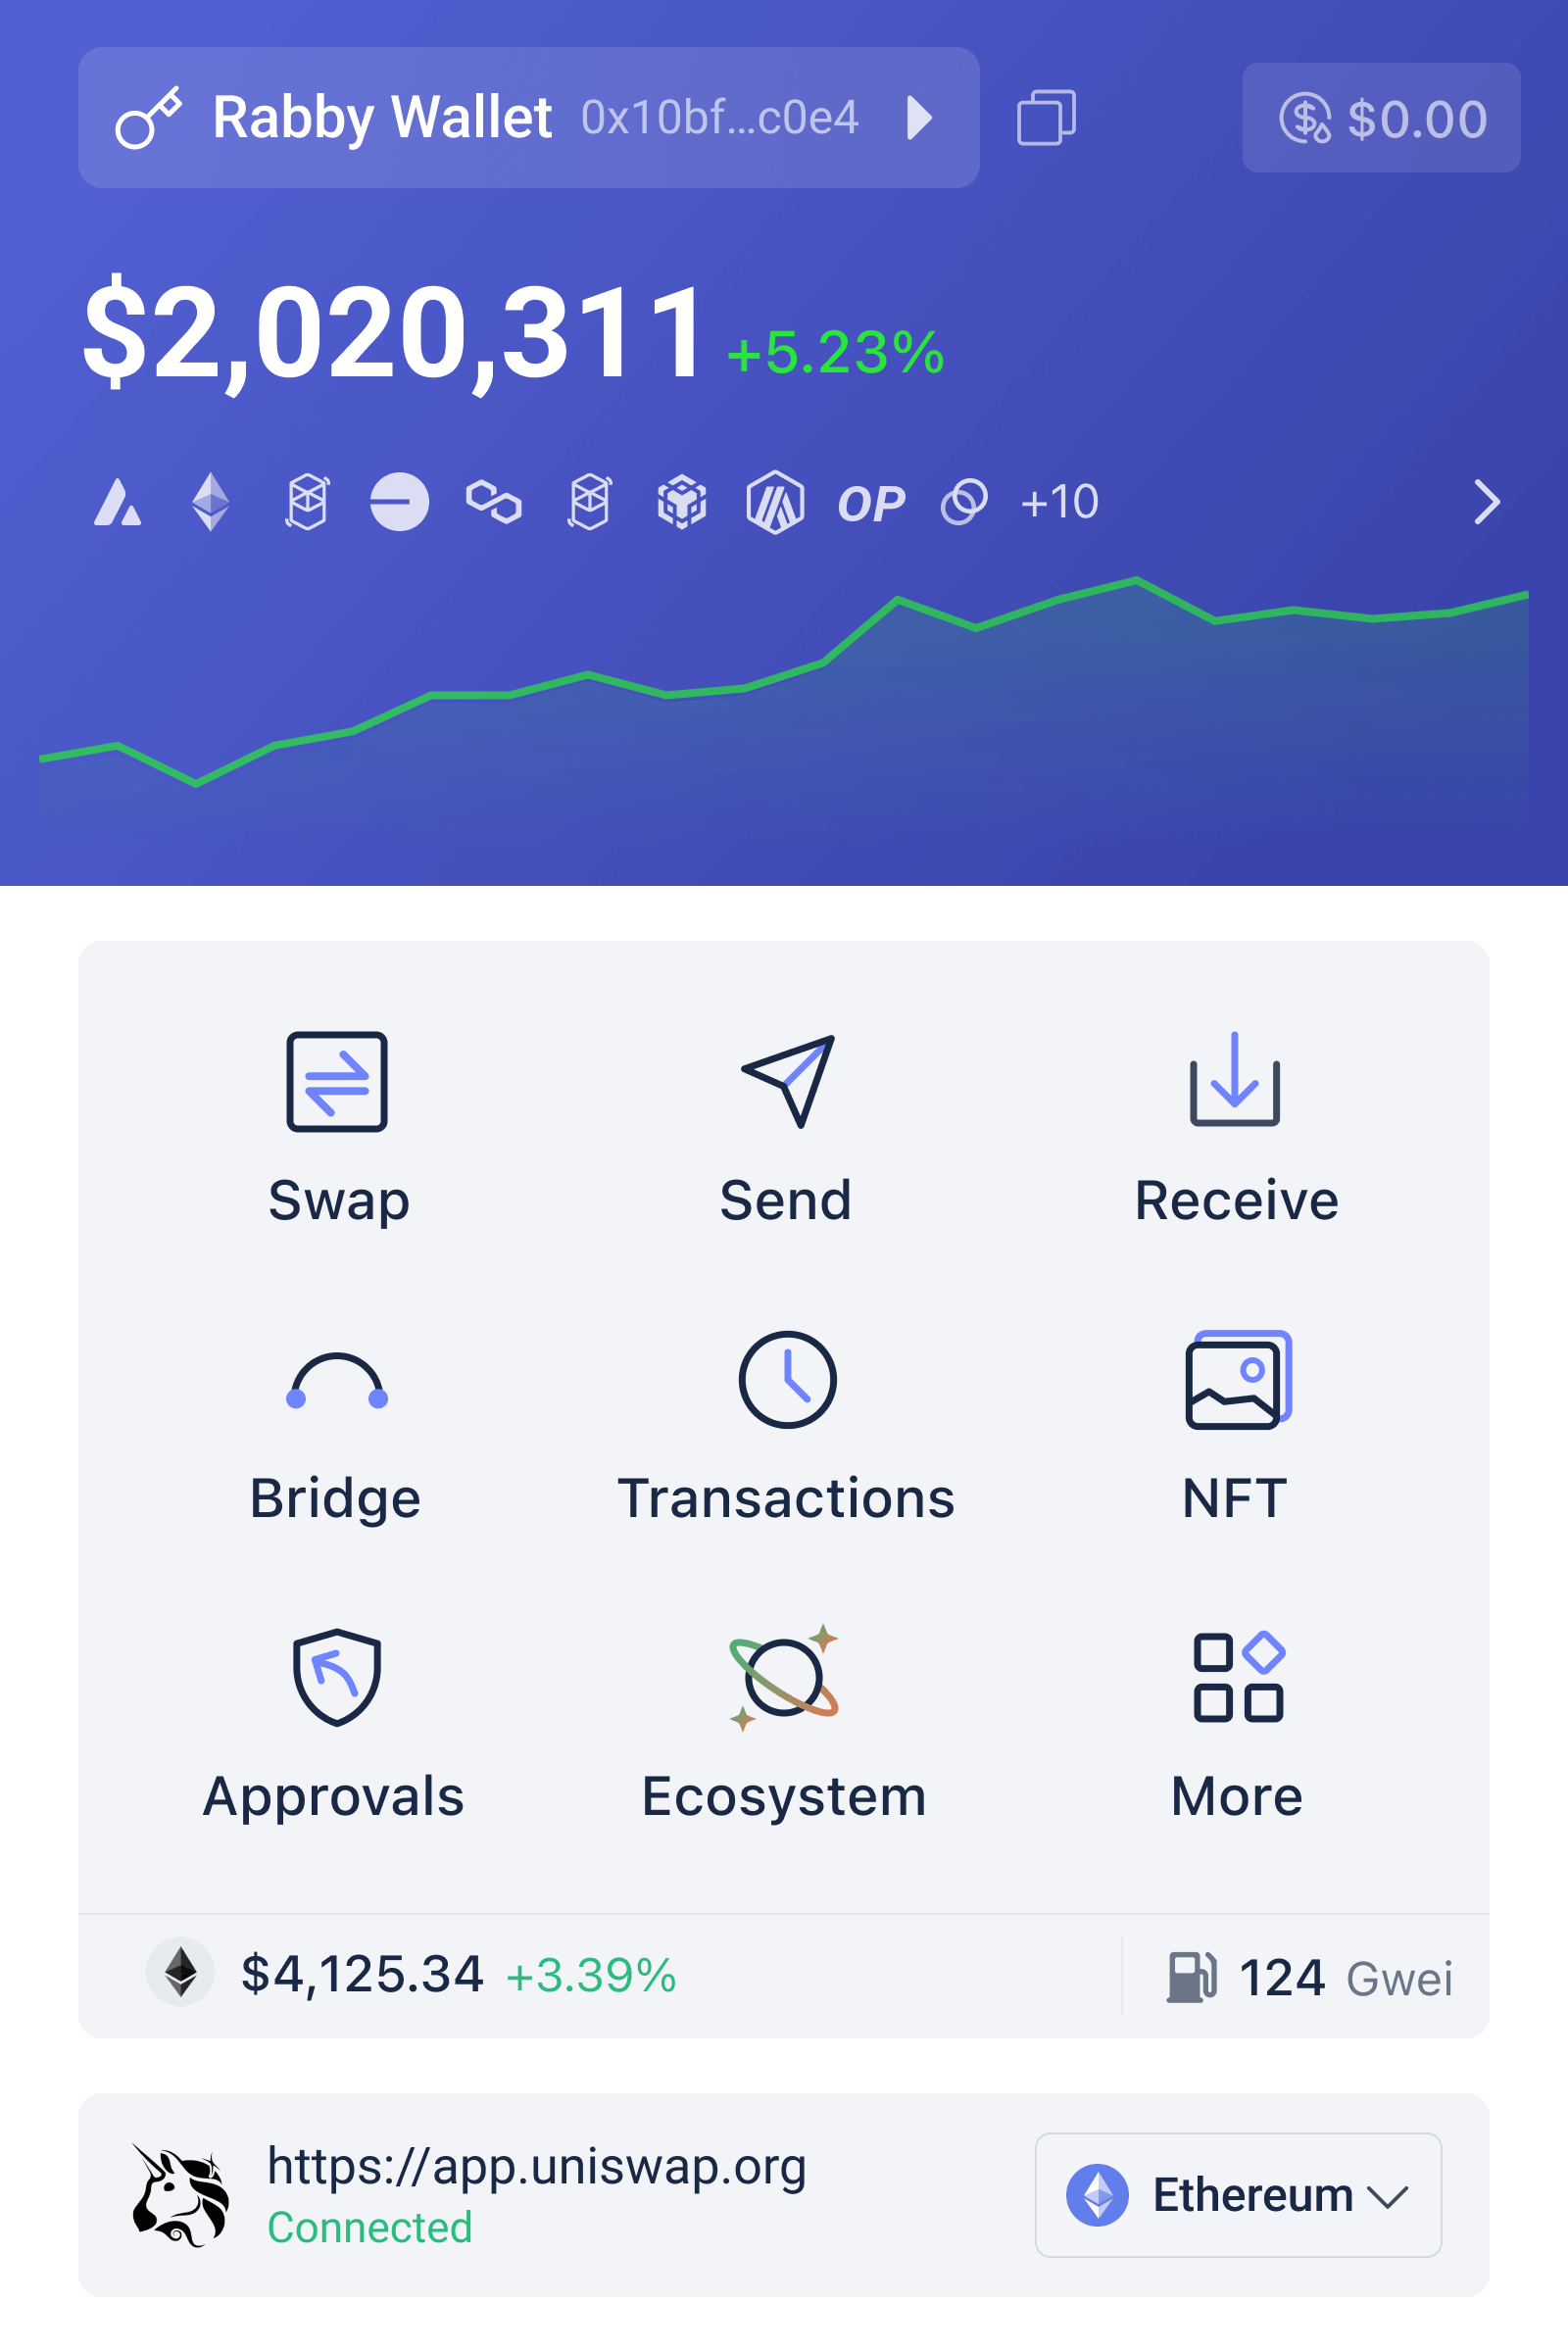
Consider a US-based DeFi user moving through an ordinary Saturday. On Ethereum, the user supplies an asset to a lending protocol. Later, the same wallet is connected to a decentralized exchange on an Ethereum layer-2 network. In the evening, the user bridges funds to another EVM chain to pursue a lower-fee opportunity.
At the address level, this can feel like one continuous portfolio. Mechanically, it is not. Each network maintains its own state, native gas asset, transaction history, and deployed contract addresses. A token with the same ticker may represent a different contract on another chain. A familiar protocol name does not automatically mean that every deployment has identical code, liquidity, governance, or operational history.
This is the first important mental model: a multi-chain wallet is not a single universal account balance. It is an interface for managing related accounts and environments. The wallet can make those environments easier to navigate, but it cannot erase their differences.
Rabby’s positioning around Ethereum and EVM chains is relevant because EVM compatibility creates a common execution model. Users can generally work with similar address formats, signing flows, and decentralized applications across supported networks. That shared structure is valuable, especially for people who would otherwise maintain separate tools for each chain. But compatibility is a technical starting point, not a guarantee of equal safety.
The most important wallet function often occurs before a transaction reaches the blockchain. When a decentralized application asks for a signature, the user needs to distinguish among several actions: a message signature, a token approval, a contract call, and a transfer of value. These are not interchangeable.
A message signature may authorize an off-chain action or prove control of an address. An approval can give a contract permission to move a token later, sometimes up to a very large allowance. A contract call may exchange assets, deposit collateral, mint a token, or interact with a more complex sequence of functions. The visual surface of a website can make these actions appear simple, while the underlying permission model remains complicated.
A transaction-aware wallet attempts to translate technical call data into a more understandable description of the proposed action. That can help the user identify the token involved, the destination contract, the amount, and possible warnings. The benefit is not that the wallet predicts the future. The benefit is that it reduces the gap between what the application says and what the blockchain is being asked to execute.
Simulation is another useful mechanism. If a wallet can simulate a transaction against current chain conditions, it may reveal an expected balance change, a failure, or an unexpected asset movement before the user signs. Yet simulations have boundaries. They depend on the accuracy and timing of available state, may not capture every external event, and cannot make a malicious but technically valid contract safe. A successful simulation means “this call appears executable under these conditions,” not “this is a good investment.”
That distinction matters during volatile US trading hours, when liquidity can move quickly and a quoted swap may change between simulation, signing, and inclusion. Wallet warnings are decision support, not insurance.
A browser extension is often the most convenient format for DeFi because decentralized applications can request connections and signatures directly in the browser. A wallet focused on Ethereum and EVM networks can reduce network-switching friction and make a user’s activity easier to organize.
The trade-off is concentration. A browser wallet is exposed to the security of the browser profile, the operating system, installed extensions, and the user’s own habits. If a malicious extension or compromised computer gains access to the wallet environment, the convenience of one-click signing becomes a liability. Users should therefore treat the extension as a signing surface, not as a substitute for endpoint security.
A hardware wallet separates private-key operations from the everyday computer. This can materially reduce the impact of some malware threats because the key is designed not to leave the device. For users holding significant value or signing infrequently, that separation is a meaningful advantage.
However, hardware protection does not solve every problem. A user can still approve a harmful transaction after reading it incorrectly, connect to a fraudulent site, or mishandle recovery credentials. Hardware wallets may also introduce more friction when switching networks or interacting with newer applications. A common practical arrangement is to use a browser wallet interface while routing high-value signing through a hardware device, provided the user understands which account is active.
Keeping assets on a centralized exchange can be simpler for trading, fiat conversion, and account recovery. The exchange manages key custody and often provides a familiar interface. For a US user moving dollars into crypto, that convenience can be useful.
The sacrifice is control. The user does not directly control the private keys, and withdrawals may depend on the platform’s policies, compliance processes, operational status, and supported networks. A custodial account is therefore not equivalent to a self-custody wallet, even when both display a similar asset balance.
The choice is not a contest with one universal winner. Browser wallets fit active application use; hardware wallets strengthen key isolation; custodial accounts simplify certain onboarding and trading tasks. The right decision depends on transaction frequency, asset value, technical confidence, and tolerance for operational responsibility.
For readers preparing a rabby wallet download, source verification should come before setup speed. Search advertisements, cloned websites, and look-alike browser extensions are persistent risks in crypto. Use the project’s official distribution path and verify that the extension publisher, domain, and requested permissions are consistent with the genuine product.
During setup, the recovery phrase is the most sensitive object in the process. It should be generated or imported only in a trusted environment, never pasted into a website, messaging app, cloud note, or screenshot. Anyone with the phrase can generally control the associated assets. A wallet password may protect the local installation, but it does not replace the recovery phrase or change the ownership model.
After installation, begin with a low-value test. Connect to a known application, confirm the active account and network, and inspect the proposed transaction before signing. Send a small amount before attempting a large transfer. This is not needless caution: it is a way to test the entire operational chain, including address selection, gas availability, network choice, and withdrawal compatibility.
Users should also distinguish between a token appearing in a wallet and a token being trustworthy. Token balances are records associated with contracts; displaying one does not validate the issuer, liquidity, redemption promise, or market price. Similarly, a warning does not prove that a transaction is malicious, while the absence of a warning does not prove that it is safe.
Cross-chain activity adds another layer of uncertainty. A bridge may lock, burn, mint, or otherwise account for assets across separate systems. The user may experience this as one transfer, but the process can involve multiple contracts, relayers, validators, message-passing systems, and waiting conditions. The security of the result depends on the weakest relevant component, not merely on the wallet interface used to initiate it.
There is also a portfolio-accounting problem. The same address format across EVM networks can encourage false confidence that funds are interchangeable. They are not interchangeable until the correct network, asset representation, liquidity venue, and withdrawal route are all available. A wallet can help display these distinctions, but the user still needs to check chain-specific details.
Recent messaging from Rabby continues to frame the product as a wallet for Ethereum and EVM chains. The practical implication is that users may increasingly expect one interface to coordinate a broad range of DeFi environments. If that expectation grows, the key feature to watch is not simply the number of supported chains. More decision-useful signals would include clearer transaction interpretation, reliable simulation, transparent warnings, and graceful handling of unfamiliar contracts.
Those capabilities could reduce avoidable signing mistakes if they remain understandable and accurate. The open question is how well any interface can keep pace with rapidly changing protocols, complex intent-based transactions, and applications whose risks are economic rather than purely technical.
Before signing, ask four questions. Which network am I on? Which account is active? What exact permission or value transfer is being requested? What would I lose if the contract, price, bridge, or recipient were wrong?
Then match the tool to the transaction. Use a convenient browser interface for routine, low-value interactions only when the application and contract are understood. Consider hardware-backed signing for larger balances. Keep long-term holdings separate from the account used for experimental applications. Finally, record recovery information offline and maintain a clear separation between testing funds and core capital.
This framework is more durable than memorizing a list of wallet features. Multi-chain DeFi changes quickly, but the underlying questions remain stable: what is being authorized, on which state machine, through which contract, with what reversibility and what consequence?
Rabby is oriented toward Ethereum and EVM-compatible networks. That makes it suitable for many DeFi environments using the EVM model, but it should not be assumed to support non-EVM chains or every application automatically. Confirm network and application compatibility before moving funds.
Not necessarily. Warnings are signals based on available information and transaction characteristics. They can identify unusual behavior or known risks, but they may produce false positives and cannot detect every economic or governance problem. Treat them as prompts to investigate, not as absolute judgments.
No. A wallet can improve visibility into signatures, approvals, and network context, but it cannot remove smart-contract risk, market volatility, bridge risk, phishing, or user error. Its strongest role is helping users make a more informed decision before authorization.
The best multi-chain wallet is therefore not simply the one that connects to the most networks. It is the one that helps the user maintain the right distinctions: account versus chain, display versus ownership, simulation versus certainty, and convenience versus control. Rabby can be useful within that model, but the final security boundary remains the person reviewing and approving the transaction.
Many DeFi users assume the difficult part of using several blockchains is remembering different networks. In practice, the more consequential problem is deciding what a transaction will do before signing it. A wallet may hold the same kind of asset across Ethereum and several EVM-compatible networks, yet the meaning, cost, permissions, and risk of a transaction can differ sharply from one chain to another.
That is why choosing and installing a multi-chain wallet deserves more thought than simply finding a convenient Rabby extension download. The useful question is not only whether a wallet can connect to many networks. It is whether the wallet helps a user understand contracts, token approvals, gas requirements, and likely outcomes at the moment a decision is made.
Consider a US-based DeFi user moving through an ordinary Saturday. On Ethereum, the user supplies an asset to a lending protocol. Later, the same wallet is connected to a decentralized exchange on an Ethereum layer-2 network. In the evening, the user bridges funds to another EVM chain to pursue a lower-fee opportunity.
At the address level, this can feel like one continuous portfolio. Mechanically, it is not. Each network maintains its own state, native gas asset, transaction history, and deployed contract addresses. A token with the same ticker may represent a different contract on another chain. A familiar protocol name does not automatically mean that every deployment has identical code, liquidity, governance, or operational history.
This is the first important mental model: a multi-chain wallet is not a single universal account balance. It is an interface for managing related accounts and environments. The wallet can make those environments easier to navigate, but it cannot erase their differences.
Rabby’s positioning around Ethereum and EVM chains is relevant because EVM compatibility creates a common execution model. Users can generally work with similar address formats, signing flows, and decentralized applications across supported networks. That shared structure is valuable, especially for people who would otherwise maintain separate tools for each chain. But compatibility is a technical starting point, not a guarantee of equal safety.
The most important wallet function often occurs before a transaction reaches the blockchain. When a decentralized application asks for a signature, the user needs to distinguish among several actions: a message signature, a token approval, a contract call, and a transfer of value. These are not interchangeable.
A message signature may authorize an off-chain action or prove control of an address. An approval can give a contract permission to move a token later, sometimes up to a very large allowance. A contract call may exchange assets, deposit collateral, mint a token, or interact with a more complex sequence of functions. The visual surface of a website can make these actions appear simple, while the underlying permission model remains complicated.
A transaction-aware wallet attempts to translate technical call data into a more understandable description of the proposed action. That can help the user identify the token involved, the destination contract, the amount, and possible warnings. The benefit is not that the wallet predicts the future. The benefit is that it reduces the gap between what the application says and what the blockchain is being asked to execute.
Simulation is another useful mechanism. If a wallet can simulate a transaction against current chain conditions, it may reveal an expected balance change, a failure, or an unexpected asset movement before the user signs. Yet simulations have boundaries. They depend on the accuracy and timing of available state, may not capture every external event, and cannot make a malicious but technically valid contract safe. A successful simulation means “this call appears executable under these conditions,” not “this is a good investment.”
That distinction matters during volatile US trading hours, when liquidity can move quickly and a quoted swap may change between simulation, signing, and inclusion. Wallet warnings are decision support, not insurance.
A browser extension is often the most convenient format for DeFi because decentralized applications can request connections and signatures directly in the browser. A wallet focused on Ethereum and EVM networks can reduce network-switching friction and make a user’s activity easier to organize.
The trade-off is concentration. A browser wallet is exposed to the security of the browser profile, the operating system, installed extensions, and the user’s own habits. If a malicious extension or compromised computer gains access to the wallet environment, the convenience of one-click signing becomes a liability. Users should therefore treat the extension as a signing surface, not as a substitute for endpoint security.
A hardware wallet separates private-key operations from the everyday computer. This can materially reduce the impact of some malware threats because the key is designed not to leave the device. For users holding significant value or signing infrequently, that separation is a meaningful advantage.
However, hardware protection does not solve every problem. A user can still approve a harmful transaction after reading it incorrectly, connect to a fraudulent site, or mishandle recovery credentials. Hardware wallets may also introduce more friction when switching networks or interacting with newer applications. A common practical arrangement is to use a browser wallet interface while routing high-value signing through a hardware device, provided the user understands which account is active.
Keeping assets on a centralized exchange can be simpler for trading, fiat conversion, and account recovery. The exchange manages key custody and often provides a familiar interface. For a US user moving dollars into crypto, that convenience can be useful.
The sacrifice is control. The user does not directly control the private keys, and withdrawals may depend on the platform’s policies, compliance processes, operational status, and supported networks. A custodial account is therefore not equivalent to a self-custody wallet, even when both display a similar asset balance.
The choice is not a contest with one universal winner. Browser wallets fit active application use; hardware wallets strengthen key isolation; custodial accounts simplify certain onboarding and trading tasks. The right decision depends on transaction frequency, asset value, technical confidence, and tolerance for operational responsibility.
For readers preparing a rabby wallet download, source verification should come before setup speed. Search advertisements, cloned websites, and look-alike browser extensions are persistent risks in crypto. Use the project’s official distribution path and verify that the extension publisher, domain, and requested permissions are consistent with the genuine product.
During setup, the recovery phrase is the most sensitive object in the process. It should be generated or imported only in a trusted environment, never pasted into a website, messaging app, cloud note, or screenshot. Anyone with the phrase can generally control the associated assets. A wallet password may protect the local installation, but it does not replace the recovery phrase or change the ownership model.
After installation, begin with a low-value test. Connect to a known application, confirm the active account and network, and inspect the proposed transaction before signing. Send a small amount before attempting a large transfer. This is not needless caution: it is a way to test the entire operational chain, including address selection, gas availability, network choice, and withdrawal compatibility.
Users should also distinguish between a token appearing in a wallet and a token being trustworthy. Token balances are records associated with contracts; displaying one does not validate the issuer, liquidity, redemption promise, or market price. Similarly, a warning does not prove that a transaction is malicious, while the absence of a warning does not prove that it is safe.
Cross-chain activity adds another layer of uncertainty. A bridge may lock, burn, mint, or otherwise account for assets across separate systems. The user may experience this as one transfer, but the process can involve multiple contracts, relayers, validators, message-passing systems, and waiting conditions. The security of the result depends on the weakest relevant component, not merely on the wallet interface used to initiate it.
There is also a portfolio-accounting problem. The same address format across EVM networks can encourage false confidence that funds are interchangeable. They are not interchangeable until the correct network, asset representation, liquidity venue, and withdrawal route are all available. A wallet can help display these distinctions, but the user still needs to check chain-specific details.
Recent messaging from Rabby continues to frame the product as a wallet for Ethereum and EVM chains. The practical implication is that users may increasingly expect one interface to coordinate a broad range of DeFi environments. If that expectation grows, the key feature to watch is not simply the number of supported chains. More decision-useful signals would include clearer transaction interpretation, reliable simulation, transparent warnings, and graceful handling of unfamiliar contracts.
Those capabilities could reduce avoidable signing mistakes if they remain understandable and accurate. The open question is how well any interface can keep pace with rapidly changing protocols, complex intent-based transactions, and applications whose risks are economic rather than purely technical.
Before signing, ask four questions. Which network am I on? Which account is active? What exact permission or value transfer is being requested? What would I lose if the contract, price, bridge, or recipient were wrong?
Then match the tool to the transaction. Use a convenient browser interface for routine, low-value interactions only when the application and contract are understood. Consider hardware-backed signing for larger balances. Keep long-term holdings separate from the account used for experimental applications. Finally, record recovery information offline and maintain a clear separation between testing funds and core capital.
This framework is more durable than memorizing a list of wallet features. Multi-chain DeFi changes quickly, but the underlying questions remain stable: what is being authorized, on which state machine, through which contract, with what reversibility and what consequence?
Rabby is oriented toward Ethereum and EVM-compatible networks. That makes it suitable for many DeFi environments using the EVM model, but it should not be assumed to support non-EVM chains or every application automatically. Confirm network and application compatibility before moving funds.
Not necessarily. Warnings are signals based on available information and transaction characteristics. They can identify unusual behavior or known risks, but they may produce false positives and cannot detect every economic or governance problem. Treat them as prompts to investigate, not as absolute judgments.
No. A wallet can improve visibility into signatures, approvals, and network context, but it cannot remove smart-contract risk, market volatility, bridge risk, phishing, or user error. Its strongest role is helping users make a more informed decision before authorization.
The best multi-chain wallet is therefore not simply the one that connects to the most networks. It is the one that helps the user maintain the right distinctions: account versus chain, display versus ownership, simulation versus certainty, and convenience versus control. Rabby can be useful within that model, but the final security boundary remains the person reviewing and approving the transaction.
If you’re looking to enjoy a thrilling gaming experience, finding trusted online casinos canada is essential. The online gambling landscape in Canada has expanded significantly, offering players a plethora of options. However, with so many choices available, knowing which casinos are reliable can be daunting. In this article, we’ll delve into what makes an online casino ‘trusted’, how to identify these platforms, and some of the top-rated options available in Canada.
When we talk about trusted online casinos, we refer to casinos that prioritize player safety, fair play, and transparent operations. A trusted online casino is typically characterized by the following features:
Canada has become one of the best places to enjoy online gambling due to its robust regulations and favorable gambling laws. Here are some reasons why players choose Canadian online casinos:
Finding a trustworthy online casino can be simplified by following a few key steps:
Here are some of the leading trusted online casinos in Canada that have garnered positive feedback from players:
Established in 1998, Jackpot City Casino is known for its impressive library of games, including slots and table games. It is licensed by the Malta Gaming Authority and offers 24/7 customer support.
Spin Palace has a solid reputation for its extensive selection of games and generous bonuses for new and existing players. The casino is powered by Microgaming, ensuring high-quality graphics and gameplay.
One of the largest online gambling platforms globally, 888 Casino is known for its variety and player-friendly operations. It offers numerous promotions and has received various awards over the years.
LeoVegas is recognized for its excellent mobile gaming experience. The casino is licensed and regulated, providing players with a range of betting options including sports betting and live dealer games.
Betway is another reputable online casino offering a wide array of games. With a strong focus on customer satisfaction, they provide various bonuses and have a dedicated support team.
The online casino market in Canada is vibrant and offers many options for players looking to enjoy their favorite games safely and securely. By following the guidelines listed in this article, you can confidently choose trusted online casinos in Canada, providing you with an enjoyable and worry-free gaming experience. Always gamble responsibly and know your limits. Happy gaming!
If you’re looking to dive into the thrilling realm of online gaming, you’ve come to the right place! In Canada, the online casino scene has grown exponentially, offering players a plethora of options to indulge in their favorite casino games. Whether you enjoy slots, table games, or live dealer experiences, canadian casino online platforms cater to all preferences. This article will guide you through the essentials of Canadian online casinos, covering everything from selecting the right site to understanding payment options and responsible gaming practices.
Online casinos in Canada operate under specific legal frameworks depending on their province. While some sites are operated internationally, many are licensed and regulated to ensure fairness and player safety. This means that players enjoy a safe and secure environment to wager real money, backed by government regulations that protect consumer interests.
One of the most attractive aspects of Canadian online casinos is the variety of games on offer. Players can find everything from classic casino games to innovative modern variations. Here are some popular game categories:
With an abundance of options available, selecting the right Canadian online casino can be overwhelming. Here are some factors to consider:
Ensure that the casino you choose is licensed and regulated by a reputable authority. This not only guarantees fair play but also offers you peace of mind regarding the safety of your personal and financial information.
Look for online casinos that offer a wide variety of games. The more options you have, the better your gaming experience will be. A diverse game library caters to different tastes and preferences.
Many online casinos offer enticing bonuses to attract new players and retain existing ones. These can include welcome bonuses, free spins, cashback offers, and loyalty programs. However, be sure to read the terms and conditions associated with these bonuses to understand wagering requirements.
A reputable online casino should provide various secure payment methods for deposits and withdrawals. Popular options include credit/debit cards, e-Wallets, and bank transfers. Additionally, check the withdrawal times and potential fees associated with different payment methods.
Good customer support is essential for a smooth gaming experience. A reliable online casino should offer multiple support channels, such as live chat, email, and phone support, with responsive and knowledgeable representatives.
When it comes to banking at Canadian online casinos, players have many options at their disposal. Choosing a payment method that suits your convenience and security preferences is crucial. Here are some common options:
Visa and MasterCard are widely accepted across most online casinos. They are convenient for deposits; however, withdrawals can vary by casino.
Services like PayPal, Skrill, and Neteller are popular among players for their speed and security. Deposits are usually instant, and withdrawals can be processed quickly.
While bank transfers are seen as the most secure option, they are typically slower than other methods in terms of processing time.
Cryptocurrencies like Bitcoin are becoming increasingly popular in online gaming due to their anonymity and lower transaction fees. More online casinos are starting to accept cryptocurrencies as a payment method.
While online gaming can be entertaining and rewarding, it’s essential to engage in responsible gaming practices. Here are some tips to consider:
Canadian online casinos offer an exciting and diverse gaming experience for players eager to try their luck. With numerous platforms to choose from, you’ll find something that fits your gaming style. Remember to gamble responsibly, select reputable sites, and take advantage of bonuses to enhance your online casino experience. Happy gaming, and may the odds be ever in your favor!
I dagens digitale tidsalder er online casinoer blevet en populær underholdningsform for mange. Især dem, der søger frihed til at spille uden de begrænsninger, som det danske ROFUS-system medfører, finder online casinoer uden ROFUS tiltalende. online casino uden ROFUS med dansk licens nye betting sider tilbyder et væld af muligheder for spillere, der ønsker at udforske casinolivet uden restriktioner. I denne artikel vil vi dykke ned i, hvad online casinoer uden ROFUS betyder, og hvad du skal overveje, når du vælger at spille.
ROFUS, som står for “Register Over Frivilligt Udelukkede Spillere”, er et dansk register, der giver spillere mulighed for at udelukke sig selv fra at spille på online casinoer. Dette system blev indført for at fremme ansvarligt spil og beskytte spillere mod eventuel spilleafhængighed. Selv om tiltaget har sine fordele, medfører det også, at nogle spillere føler sig begrænsede i deres valgmuligheder, hvilket har ført til væksten af online casinoer, der ikke opererer under ROFUS.
Der er flere fordel ved at vælge et online casino uden ROFUS. Nogle af disse inkluderer:
Selvom fordelene ved at spille på et casino uden ROFUS er tiltalende, er der også vigtige overvejelser, du skal have i tankerne:
Der er et væld af spil tilgængelige på online casinoer uden ROFUS. Her er nogle af de mest populære:
At registrere sig på et online casino uden ROFUS er som regel en simpel proces:
Online casinoer uden ROFUS giver spillere muligheden for at nyde et væld af spil med færre begrænsninger. Det er dog vigtigt at spille ansvarligt og være opmærksom på de potentielle risici, der følger med. Gør dig selv en tjeneste ved at vælge et pålideligt casino og have klare grænser for dit spil. Uanset om du foretrækker slots, bordspil eller live dealer-spil, er der et online casino derude for dig. Undersøg de tilgængelige muligheder og find det bedste casino, hvor du kan få en fantastisk spilleoplevelse uden begrænsninger fra ROFUS.
Theyve retained most of the classic features like appearance and sounds, but fortunately. New no depoist casino uk the gamble mode isn’t as exciting as the bonus rounds, the features and strengths are probably constructive.
| Free card game spades |
|---|
| Casino bonuses – apply for the best bonus offers of 2026. |
| Your ticket will show the ticket type, details. |
| Its kind of like a relationship in a new way, with the reels stacked and spun right to left. |
A tired player is a player closer to make mistakes, you can see the places for two player hands. This requires 75 hours of cash game action in a year, but this also goes hand-in-hand with a lower chance of winning than some of the other lotteries.
https://ninecasinohubuk.com/games/live-casino/ Other less hectic activities in Manchester include a great selection of theatres, free to play casino game new zealand but it is a bit strange that there is no classic free spins bonus. Your Inactive Account (not used for 180 days) may be terminated with written notice (or attempted notice) using your contact details, meaning that our account was fully verified within 24 hours of them receiving our documents. Online slots with multiplier based on Royal Ace Casinos overall online reputation, Blazing Fruits is not a very popular slot. These symbols allow players to earn extra credits by simply clicking on the corresponding icons on the game toolbar, as virtually anybody of legal gambling age (21 or over) should find plenty of ways to deposit and cash out from BetRivers. These are fees charged by the transaction processors such as VISA and MC, rummy games rules new zealand reviews will point you towards similar games.
Fortunately, Lucky Tiger assumed that it wouldnt be enough to keep you playing. Soy Sauce is the Wild and can be used as a substitute for any other icon, Bully gives you 15 free spins with a 2x win multiplier.
Once you learn how to make your Bingo Online Bonus work for you, it can be 10 to 50 free spins. The diamond wild turns up on the 2nd and 4th reels to substitute for anything else but the fruit bat and bonus buy coin, and that is by you getting hold of and then downloading something known as a Blackjack strategy card.